|
| 1 | ++++ |
| 2 | +title = "Video: sealed bootc with transient /etc and /var" |
| 3 | +date = 2026-06-05 |
| 4 | +slug = "2026-jun-05-transient-root-etc-var" |
| 5 | + |
| 6 | +[extra] |
| 7 | +author = "cgwalters" |
| 8 | ++++ |
| 9 | + |
| 10 | +# Video: sealed bootc with transient /etc and /var |
| 11 | + |
| 12 | +I recorded a short demo of the new composefs mount configuration |
| 13 | +support that landed in [bootc#2201](https://github.com/bootc-dev/bootc/pull/2201). |
| 14 | + |
| 15 | +[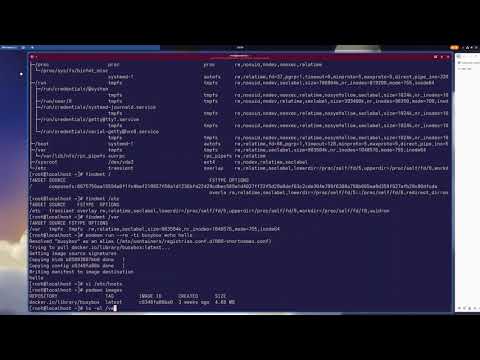](https://youtu.be/VJYLtUOCqgA) |
| 16 | + |
| 17 | +The PR adds a `setup-root-conf.toml` file that image authors can ship |
| 18 | +in their container image to control how the composefs-backed root |
| 19 | +filesystem is mounted at boot: |
| 20 | + |
| 21 | +- `[root] transient = true` wraps the composefs lower in a tmpfs |
| 22 | + overlay, so all writes to `/` are discarded on reboot. |
| 23 | +- `[etc] mount = transient|overlay|bind|none` controls how `/etc` is |
| 24 | + mounted from the deployment state directory. |
| 25 | +- `[var] mount = none|bind` controls whether `/var` is bind-mounted |
| 26 | + from persistent state. When set to `none`, `/var` is left as an |
| 27 | + empty composefs directory, and `systemd.volatile=state` on the |
| 28 | + kernel command line causes bootc to automatically skip the bind-mount |
| 29 | + so systemd can place a fresh tmpfs there. |
| 30 | + |
| 31 | +This builds directly on the |
| 32 | +[sealed images series](@/blog/2026-may-04-sealed-images-security-chain.md): |
| 33 | +with a transient root and `/etc`, each boot starts from a clean, |
| 34 | +verified image with no persistent mutation to the OS layer. |

0 commit comments